1. Abstract
The security is crucial and critical part of the data model design. It should be considered during the design phase already.
In the following chapters clarifications and best practice approaches are described.
This document is not a replacement for the manual. It will give some impression/ideas. It is recommended to read about the different security settings in the manual before this document is read.
2. Common Understanding
2.1 Overview
The security in Board covers following objects:
- Database
- Entities
- Cubes
- Capsule Folders or Folder Profiles
- Users
- (Rules)
- (Procedures)
For screens, no native security is available.
2.2 Users
The first created user is the Administrator user with a password. This user has full access to all settings and should not be restricted at all. Further full-access users (like Administrator user) can be generated (depending on the number of licenses).
For technical tasks (like scheduled procedures) it is recommended to create a TECHNICAL User with USER license. This user should not have access to capsules, should not be able to access layouts and screen selections but can run system critical tasks (see Security Profile or Features (IDP)), e.g. backups. This user might be used in the scheduled tasks and therefore, it is a password user.
The passwords should have a very secure password and should be changed regularly. This applies to all password users. Note that if the user is used for scheduled tasks, that each time the password is changed the scheduled tasks will need to be updated
For the other users it is highly recommended to use Single-Sign-On (SSO) authentication like Active Directory, Windows authentication, Office 365 and so on.
For the IDP it is possible to add more than one Identity Provider. Therefore, it is recommended for the Board employees to add Board’s identity provider. This will secure the access and reduces the need to have user/password user which are less secure. Especially as Board employees usually have many permissions or even full access.
There are at least three roles, features, security profiles expected:
2.3 Security Settings
2.3.1 Data Model Security – Profile
The data model security is used to restrict the database access (capabilities, entities, cubes).

See
https://help.board.com/v14/docs/the-database-security-section
for detailed information on the different settings.
The “Add Security Selection” feature stores fixed Entity selections and can create problems if internal element IDs change (see Fixed Entity Selections). For Entity restrictions, use “Select Entity Based on Cube” in combination with a User Entity and the Custom Selection Script “Select User=@User”.
A good design for permission cubes is that the access is prevented when a cube is empty (e.g. somebody cleared and so …). This already applies for the entities. For the cube visibility the same logic should be applied but can be done differently (not recommended), i.e. for the grant cube access the “<> 0” option and for the deny data entry the “= 0” option should be used.
It is highly recommended to set permission cubes to read only for the users which are affected by them.
Recommended Architecture — Database Security and Cube Visibility
The recommended architecture separates two responsibilities:
- Database Security — the stable Entity-level perimeter. Data Model Security Profiles and Roles, Custom Selection Scripts (e.g. Select User=@User) and Select Entity Based on Cube define which Entity members a user can access. These selections are calculated at login and remain fixed for the whole session: a change to the underlying security Cube becomes effective only at the user’s next login.
- Cube Visibility — dynamic cell-level read/write access inside that perimeter. Access conditions (“Grant cells access where”) and Locking conditions (“Deny cell editing where”) reference numeric permission Cubes, for example a Cube dimensioned by User and Department. When a permission Cube is updated, refreshing the Screen applies the new data visibility and Data Entry permissions without a new login.
Permissions that must change during an active session therefore belong in Cube Visibility, while mandatory boundaries that do not change during the session belong in Database Security. Select Entity Based on Cube is not a mechanism for in-session permission changes.
To configure Cube Visibility, open the Data Model Security Profile, select the Cube in the Cube visibility table, set its access level (Read/Write, Read only or No access) and define the Access and Locking conditions in the advanced access settings. See the Board Manual (Cube visibility) for details.
Limits of Cube Visibility
Cube Visibility does not replace Database Security and does not change the Entity selection it establishes. In particular:
- Pagers and Selectors may still display Entity members outside the Cube Visibility perimeter, while Layout-based objects show data according to the Cube Visibility conditions.
- Cube Visibility does not automatically restrict every Procedure Dataflow.
Write permissions and the Deep Locker
Implement Data Entry restrictions with the Locking condition (“Deny cell editing where”) in Cube Visibility, so the restriction is maintained in the Data Model security configuration rather than separately in individual Layouts. The Locking condition is not compatible with the Deep Locker (“Cube cells locked by Cube”) configured in a Layout, so the two must not be combined. As the Deep Locker also has stricter dimensional requirements (the locking Cube cannot introduce additional dimensions), Cube Visibility with permission Cubes is the recommended approach whenever Data Entry restrictions are part of the security model.
Recommended profile settings could therefore look as follows:
- Create the ADMIN profile.
a. Name: ADMIN
b. Access Mode: Data Model Administrator
c. Security System: Builder - Create the USER profile.
a. Name: User
b. Access Mode: Read and Write (i.e. Data Entry is possible)
c. Security System: Access Denied
d. Custom Selection Script:
i. Select User=@User
ii. Select Role=@var(User Metadata Field) [for IDP, if used; multiple lines can be configured]
e. Select Entity Based on Cube: Entity restrictions that form part of the stable perimeter (applied at login).
f. Cube Visibility: Access conditions for data visibility and Locking conditions for Data Entry, based on permission Cubes (effective after a Screen refresh).
2.3.2 IDP
IDP – User
Users are managed in the User overview.
Also, in Platform authorization the user can be assigned to different instances, roles and licenses.

IDP – User Metadata
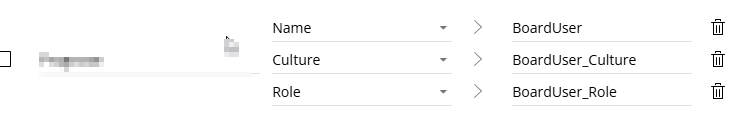
The User Meta is useful to add some more information about the user OR to use this information in the security. In the case it is used for roles it is suggested to use a Dropdown list – to prevent typos.

A user metadata field can also be used in a Custom Selection Script, e.g. Select Role=@var(Field). Like all Database Security selections, it is part of the Entity-level perimeter, and a change becomes effective at the user’s next login.
System Administration – Role
Preferably, the Default data model security profile should be used instead of adding profiles manually.
This applies at least for the ADMIN and TECHNICAL users. If possible, this should be used for the standard user profiles also.

System Administration – Features
Depending on the application design it might be recommended to DENY the layout designer and the selection editor for the standard user. Allow execution of security critical procedures should be deactivated. With the access to the layout designer the User can change the layout and might be able to see values which should not be seen. By changing the selections on a screen, the user might be able to change it and create errors or even unintended data entries. Of course, most of the cases could be prevented by setting up the security properly.
Deny the layout designer and the selection editor can be set on each screen individually also. It is not recommended to use it (intensively) because it also applies to full-access users (like Administrator user). They usually rely on the access to the layout and the selection editor in test and error cases.
For the TECHNICAL user, all settings should be denied/disallowed. Only the Allow execution of security critical procedures must be allowed.
For the ADMIN nothing should be denied or disallowed.

2.3.3 On-Premise
System Administration – User
It is possible to set Entity selections per user and data model, but these are fixed Entity selections (see Fixed Entity Selections) and are not recommended. Use Select Entity Based on Cube in the Data Model Security instead to define the Entity-level perimeter.

System Administration – Profiles
The Security profiles combine the settings of Role and Feature (see checkmarks) of the IDP instances. In addition, the license needs to be assigned. Therefore, the same recommendations as for the IDP apply:
Checkmarks
Depending on the application design it might be recommended to DENY the layout designer and the selection editor for the standard user. Allow execution of security critical procedures should be deactivated. With the access to the layout designer the User can change the layout and might be able to see values which should not be seen. By changing the selections on a screen, the user might be able to change it and create errors or even unintended data entries. Of course, most of the cases could be prevented by setting up the security properly.
Deny the layout designer and the selection editor can be set on each screen individually also. It is not recommended to use it (intensively) because it also applies to full-access user (like Administrator user). They usually rely on the access to the layout and the selection editor in test and error cases.
For the TECHNICAL user, all settings should be denied/disallowed. Only the Allow execution of security critical procedures must be allowed.
For the ADMIN nothing should be denied or disallowed.
Data Model
Preferably, the Default data model security profile should be used instead of adding profiles manually.
This applies at least for the ADMIN and TECHNICAL users. If possible, this should be used for the standard user profiles also.
2.3.4 System Administration – Folder Profile Security
The folder profile security is deactivated by default but provides a lot more possibilities than the default capsule security, i.e. full-access folder selection.
One or more folder security profiles can be assigned to a security profile (On Premise) or role (IDP). It is additive, i.e. if two profiles have different security settings for the same folder, then the highest permission wins.
See
https://help.board.com/docs/the-folder-security-section
for more information.
Following permissions are available:
- Play only: Cannot switch to Design mode.
- Read only: Can switch to Design mode but cannot save changes.
- Read & Write: Can create, delete and change capsules.
At least one profile is required:
- ADMIN
- Folder: Capsules (e.g. C:\Board\Capsules)
- Mode: Read & Write
- Apply to all Subfolders: Activated
For the further design it is recommended to create folder profiles depending on application roles (But usually different from the roles within an application).
Example:
- [Database 1] Planner: Has play access to the planning capsule for Database 1.
- [Database 1] Security Admin: Has play access to the security capsule for Database 1.
- [Database 1] Admin: Has play access to the administration capsule for Database 1.
- [Database 1] Developer: Has Read & Write access to all capsules for Database 1.

2.4 Fixed Entity Selections
A fixed entity selection is when an element is selected from the e.g. the screen selection, block selection and so on. In this case Board stores the internal element ID (not the Code nor the description) which will be dependent on the loading order.
Risk
If the order changes because the order is not controlled specifically then users might get other permissions. This is a worst-case scenario in the security. Therefore, fixed entity selections are not recommended when the entity is not fully controlled, and the internal IDs always point to the same element.
3. Profile Duplication Driver
3.1 Introduction
The main goals of the security architecture are easy maintenance and good scalability (besides, it is working).
Easy maintenance can be achieved when profiles (= data model profiles, security profiles, security role, security features) can be used for multiple users and the profiles are not named like the users, e.g. the user driven profile creation should be prevented. Also, the creation of profiles depending on all possible mathematical combinations of data models and/or capsule should be prevented/reduced.
This topic becomes relevant when some databases exist and users have very individual access (Access, No Access, Entities, Cubes etc.).
3.2 Drivers for multiple profiles
What are drivers for multiple profiles (and which are not)?
Driver | Y/N | Description |
|---|
Entity | N | In the data model security, it is possible to define Select Entity Based On Cube restrictions for each entity. User entity is usually required. On-Premise: In the User administration a selection for each data model and user can be set. User entity is not required but it is a fixed entity selection. IDP: This selection setting is available on the Role and therefore not helpful to reduce the number of roles. Also, user metadata can be injected in the security script to set the restrictions (which might not be readable because of displaying only codes and its length) |
Cube Visibility | N | In the data model security is possible to define the use of other cubes’ values to drive the visibility/writing access. |
Cube Write Permissions | N | In the data model security is possible to define the use of other cubes’ values to drive the visibility/writing access. |
Database Access | Y/N | The database access is defined in the Security profile (On Premise) or Roles (IDP). In the data model section, a data model can be added by using a specific data model security profile. (Y) But also, a default data model security profile can be defined (N). When the second option is used a user might get access to a database which should not be accessed. How can this be restricted? IDP: Work with user metadata, e.g. roles (No Access, Admin, Controller, …) or Access attributes (Y, N) for each data model. These attributes are connected in the data model security selection script (Select Entity = @var (ACCESS_BUDGET). Important is that the No Access or the N are not within the entity. In this case the access to the database will fail. On-Premise: Such method does not exist. |
Capsules (Default Security) | Y | The capsule security is defined in the IDP: Roles On-Premise: Security Profile. Therefore, it is the main driver for the duplication of security profiles. |
Folder Security (Alternative) | Y | The folder security (Alternative for the capsule default security) is also assigned in the IDP: Roles On-Premise: Security Profile. Therefore, it is a main driver for the duplication of security profiles. The legacy ~Security database could manage this assignment through the cube Assigned Folder Profiles, but it is no longer supported and not recommended (see On-Premise: ~Security or ~DBName database). |
Screens | - | Cannot be managed individually by security |
License | Y/N | The license is set in the IDP: User management and therefore, it is not a driver. (N) On-Premise: Security Profile and therefore, it is a driver. (Y) |
Other settings | Y | Other settings like Deny Layout Designer, Deny Selection Editor, do not allow execution of security critical Procedures, … are also driving the duplication but are usually not relevant as they have the same settings for most of the profiles. |
3.3 Conclusion
It is recommended to prevent profile duplication. Use the Default Data Model Security Profile, Select Entity Based on Cube for the stable Entity-level perimeter, and Cube Visibility with permission Cubes for dynamic cell-level read/write access within that perimeter.
Folder Profile Security remains a driver for profile duplication. The legacy ~Security database is not a recommended way to avoid it.
4. Security Application
4.1 Overview
A security application follows the architecture described in Data Model Security – Profile: Select Entity Based on Cube defines the stable Entity-level perimeter, calculated at login, and Cube Visibility with permission Cubes controls dynamic cell-level read/write access within that perimeter.
Maintaining the security with cubes, requires creating an application and a frontend for the administration. The administration should only be accessible for certain users. Therefore, a separate capsule might be required.
4.2 Requirements
- Define key users who can change the security for other users besides full-access users (like Administrator user). The key users are not allowed to extend their own permissions. This can be achieved by using a cube visibility cube on User x User [Security] (CLC_MAP User x User [Security Entry]). Also, all security data entry cubes should be secured by the cube visibility by a cube which contains the information which users are key users ([SEC] INP_Key User). This part is optional but should be considered when many users need to be managed.
- Set visibility access for entities. There might be several entities within one tree for which an input is required. All these permissions need be calculated to one level. E.g. for cost center hierarchy:
- Cost Center (Most required detailed level. Therefore, it is used for the Select Entity Based On Cube Entity Security in the data model security)
- Plant
- Legal Entity
- All Cost Centers
- Set writing access for entities. These settings will also be used to calculate the entity visibility.
- Set special permissions, e.g.
- is allowed to see sales only
- or only production
- or can control the workflow
- or is only able to submit a workflow
- or is allowed to upload data via smart import
- …
Example for the visibility settings for the organization tree and product tree:

In the next example is a configuration of Select Entity Based on Cube. The cost center is part of the organization tree. Due to the design of the dimensions there are 4 more hierarchies which use cost centers. The setting of the cost center is transformed to these 4 other hierarchies and is applied in the security. There is still just one setting in the frontend for the cost center hierarchy.

4.3 Database
The security frontend can be built into the application database. In the case a consolidation of permissions is required, it could make sense to create a separate database (e.g. Application_Security) which collects all the permission input, calculates the permissions and extract it. The permissions are loaded by each application database at the end.
| Advantage | Disadvantage |
|---|
Built-In Security | - Entities are already available.
- Key Users are restricted already.
| - No consolidation view
- Multiple databases could lead to higher maintenance efforts
|
Central Security Database | - Scalable solution
- Single point of entry
- Simplified user security
- Easier to manage security across sandboxes
- No common @user restriction for security admins
- Stronger, role-based access control
| - Entities need to be collected from Application databases
|
There is no recommendation. It depends on the situation/customer/setup/future.
4.4 Roles and Users
Not every setting for a user is individually for a user. Usually, an aggregation like a role could be used to simplify the settings.
In the IDP the role could be added per data model via the user metadata and @var function in the selection script .
On-Premise this is usually done be adding an aggregation entity above the user entity.
An example:
The access to certain planning areas depends on the role. In addition, it is defined whether the role has read access only, writing access (when the versions are opened) or validation rights (data entry is always open & user controls the workflow):

This setting is used for the calculation of the locking cubes. Even though there is just one input, it creates several locking cubes, depending on the role. The multiple locking cubes are required for the simplified setting of the cube visibility.

4.5 Key Users and their implications
Key Users are restricted by the same security that they are allowed to maintain. Therefore, when security configuration is performed within the application/planning database, a separate User entity is required for permission entry, for example User [Security Entry].
This entity must be populated by the same processes that populate the standard User entity, and all security data-entry cubes must be dimensioned by User [Security Entry]. When security changes are saved, a procedure is executed with full permissions, with the relevant selection steps configured to Run as administrator. Within this procedure, User [Security Entry] is mapped or switched to User, and after the required calculations the results are written to the physical permission cubes dimensioned by the standard User entity.
However, if a separate central security database is used to configure security, a replicated or duplicated User entity is normally not required. One of the main advantages of this architecture is that security administrators can be given unrestricted access to the security configuration database while retaining their restricted security in the application/planning database(s). The procedure that deploys the security changes can then use Run as administrator to bypass the security administrator’s own application security when applying those changes.
Therefore, the User [Security Entry] pattern primarily addresses the case where security maintenance and the security being maintained coexist in the same database. A central security database provides an alternative architecture that avoids this requirement while also offering a single point of entry and easier management of security across multiple application databases.
4.6 Visible/Writable Access
The visibility settings are calculated to the most detailed required level of each tree and feed the Select Entity Based on Cube permission Cubes, which define the Entity-level perimeter at login.
The writable settings also feed this calculation. In addition, they are used to calculate the permission Cubes referenced in the Locking condition of every Data Entry Cube, which control write access dynamically within the perimeter.
4.7 Cube Visibility
The advantage of the cube visibility are the simplified layouts in the frontend. The data entry lock is maintained in the data model security model completely. Layout/Block locking is not required in most of the cases.
In the following example the access to the cube is connected to a role which is defined in the user metadata in the IDP. Therefore, only users of certain roles are allowed to see the cube content.
In the cell editing part two cubes are used:
- Workflow: This cube contains the dimensions role, year, plant, version. In other cases, this cube might be split in the security by adding one cube each for
- Open versions
- Open plants
- Open years
- Writing permissions to the Cost Center (per User)

Keep in mind: During the development, the settings need to be checked regularly and exported/imported to other servers. Therefore, it is required to keep a certain naming convention (e.g. prefixes, abbreviation) to maintain the cube visibility easily and finding gaps fast. Data model security is NOT a part of the data model transport. Also, the permission cubes should only contain the required dimensions as bigger cubes might slow down the performance.
4.8 Security Calculation
The calculation of the security should be triggered on the save of the security AND during the night run. It should be designed in a way that all dataflows run in the most efficient way (preferably JOIN and straight).
5. Source: User Entity
There are various sources to fill the user entity automatically.
5.1 IDP: Sync to Data Model
In the IDP a synchronization of user metadata can be added. These entities will be loaded automatically (see Board manual for full details). Advantage: the name is transferred, too.

5.2 On-Premise: UsersCreated_YYYYMM.log
For On-Premise environments, new users can be added automatically to the Users entity by reading the UsersCreated_YYYYMM.log, which contains user creation events. A Data Reader can be used to load these users into the entity.
The process should preferably be scheduled before midnight and read the log file for the current month. The following custom path can be used in the Data Reader action of the procedure:
C:\Board\Dataset\Log\UsersCreated_@DateMonth.log
The login log can also be considered as a potential source, but it is not the preferred approach. Using it would mean that users are added to the Users entity only after they attempt to log in, whereas user configuration would normally be performed proactively.
The user's name must be maintained separately or loaded automatically from an appropriate source.
5.3 On-Premise: ~Security or ~DBName database (legacy)
Legacy — not recommended. The ~Security and ~DBName databases are no longer maintained nor supported since 12.6 and should not be used in new designs. Any remaining usage requires management/CoE approval.
For reference only: these databases contain a Users entity that is synchronized with the Board users automatically, and the name of a removed user receives the prefix (*). User names need to be managed manually or loaded from a separate source.
6. Special Cases
6.1 Multiple Role Concept
Most multiple role concepts can be implemented with Cube Visibility inside the existing perimeter. In some cases, however, the Entity-level perimeter defined by Select Entity Based on Cube must change. As Database Security selections are calculated at login, such a change never applies to the current session.
Customer Case
The screens are designed to show just one legal entity. The legal entity should not be part of selectors and the screen design. Therefore, the legal entity needs to be selected before.
In this case the Entity-level perimeter is changed instead of the Screens.
A Cube contains the legal entities each user may access. Initially, the first permitted legal entity is written to the security Cube used by Select Entity Based on Cube.
A Procedure with an interactive selection allows the user to choose a different legal entity and writes it to that security Cube. Changing the Cube does not change the user’s effective Entity security during the current session: the new security selection becomes effective at the next login, so the user must log out and log in again to work with the newly selected legal entity.